
Is Agentic AI Suitable for Regulated Industries Like Fintech and Healthcare?
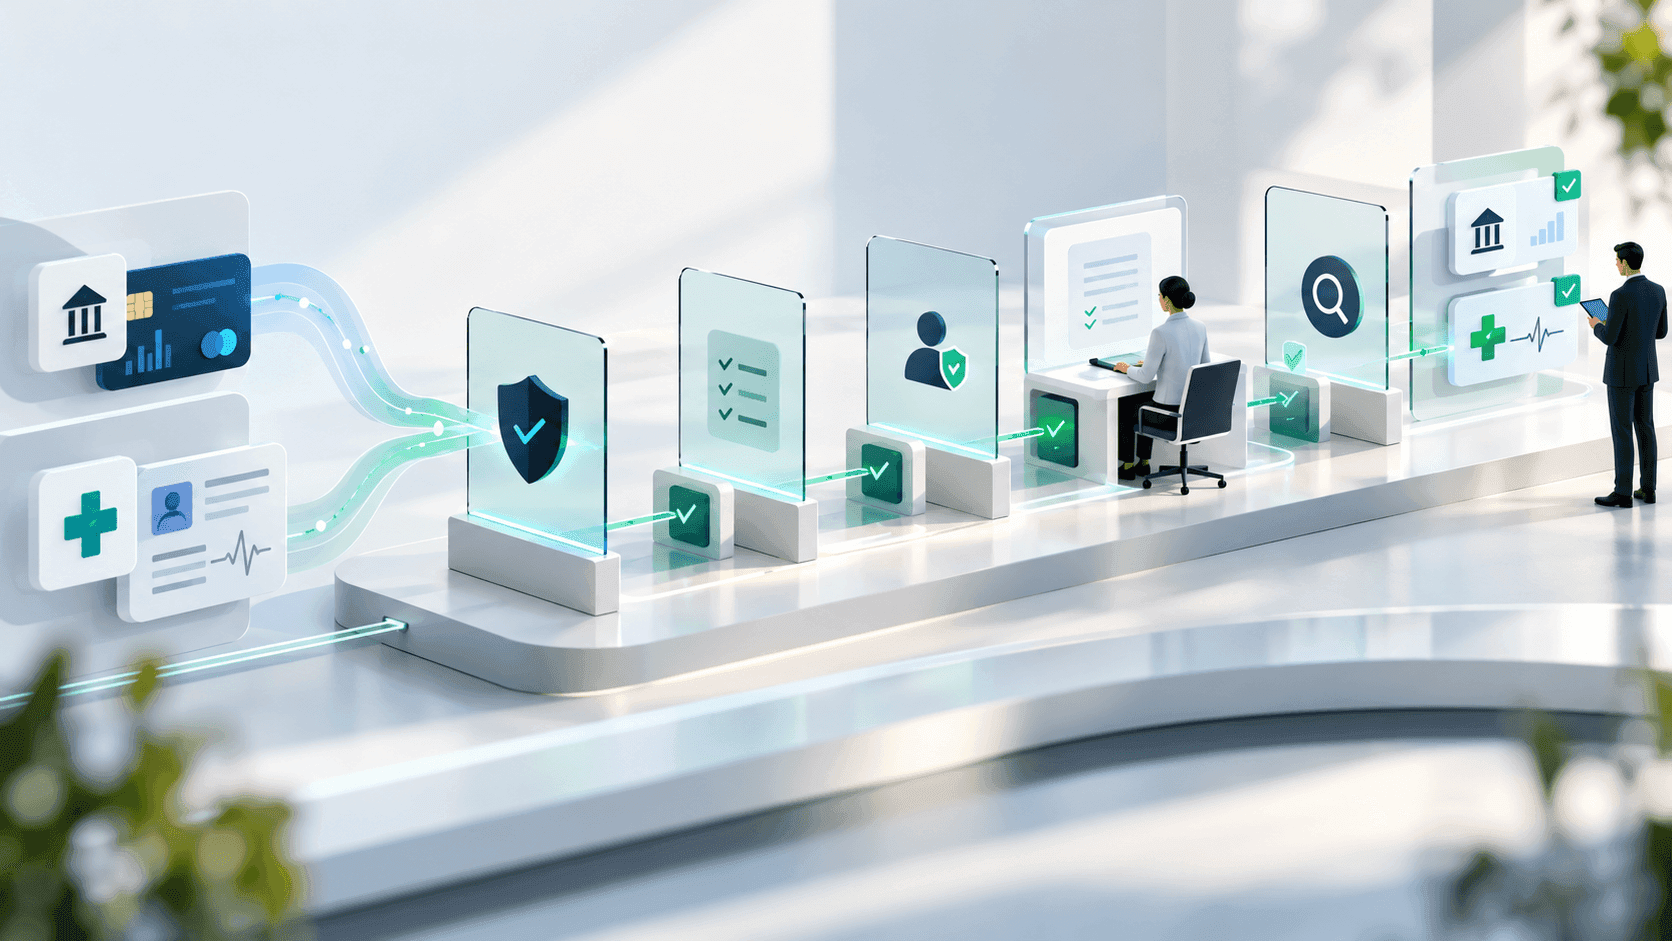
Before an AI agent can operate in fintech or healthcare, companies need to define what it can access, what it can change, and how its actions will be reviewed.
Oct 20, 2026
Yes, with conditions that need to be settled before the build. Agentic AI solutions work in fintech and healthcare when three things are defined up front: what the agent can access, which actions it is authorized to execute, and what evidence it produces for every run. High-impact actions stay behind human approval, and administrative workflows come before anything that touches a credit decision or clinical judgment. The reason to bother is volume: intake, verification and coordination work that eats hours and scales with headcount today.
The demo usually goes well. An agent reads an incoming request, pulls the relevant records, checks them against policy, drafts a response and routes it for sending. Everyone in the room can see the hours it would give back.
Then it reaches the compliance review, and the questions change. Which systems did it touch? What data left the building? Who signed off on the action it took at 2 a.m. on a Saturday? Decide what the agent will log while you design the workflow. Then compliance has something real to review before anyone writes code.
What changes when AI agents operate in regulated environments
An AI agent is a system that plans and carries out a task across several steps, choosing which tools or systems to use along the way. That is what separates it from an assistant that produces text for a person to act on. An agent reaches systems a person would have opened by hand, and produces outcomes nobody typed. The risks go beyond model selection. Four questions determine what the system can do and what happens when something goes wrong:
- What data can it reach?
- Which actions is it authorized to execute?
- What does a mistake cost, and can it be undone?
- What can detect, stop and review its behavior?
A system that reads six databases and writes to none is a different risk from one that updates a patient record or moves money, and most regulated operations already sort their work this way.
Not every workflow needs an agent. Rules-based automation handles structured inputs and predictable logic at a fraction of the oversight cost, which matters more in a regulated environment than anywhere else, because every degree of autonomy adds controls someone has to design, run and pay for. Agents earn their place when a process spans several systems, the information changes shape, and exceptions need judgment inside defined limits. We covered the broader question of what to automate and in what order in our guide to intelligent workflow automation.
The risk also comes from what the agent reads. A loan application, a patient document or a support ticket may carry instructions planted by someone outside the company. If the agent treats them as legitimate, it can use its own permissions to pull information or take an action nobody authorized. Security researcher Simon Willison calls one dangerous combination the “lethal trifecta”: access to private data, exposure to untrusted content, and a way to send information outside the system. Breaking that combination is a design decision. An agent that processes external documents should not also hold unrestricted access to internal records or arbitrary outbound destinations. Exfiltration is not the only outcome to plan for either, since an injected instruction can push a system into modifying records without any data leaving.
Four controls that make AI agents reviewable
In May 2026, CISA, the NSA and the cybersecurity agencies of the United Kingdom, Canada, Australia and New Zealand published joint guidance on the careful adoption of agentic AI services. It is security guidance rather than a legal obligation, and it is unusually specific for a multi-government document. For companies evaluating agentic AI in a regulated environment, four controls from that guidance deserve particular attention:
- A decision trace for every run. Tool calls, write actions, outputs, model and system version, and who approved or overrode each one. Retention follows the organization’s policy and the applicable rules, which is worth deciding deliberately, since logging raw inputs in a workflow that touches protected health information creates a second repository of protected data.
- Scoped permissions and a distinct identity per agent. Access to the specific systems the task needs, for as long as the task runs. Short-lived credentials instead of static secrets, and revocation when the task or the authorization ends. Shared credentials make it impossible to say which agent did what.
- Data boundaries that work in both directions. What reaches a model provider, and where the agent is allowed to send anything at all.
- Human approval before high-impact actions. The designer or the operator defines which actions require approval, never the agent itself. Lower-risk actions get limits and independent validation instead, and the system needs a way to stop further execution when something goes wrong.
Making Sense built FLEX AI with Hanwha Vision as a computer vision product, not an autonomous agent. Human reviewers identified edge cases and false positives, improving the model through successive feedback cycles. Approving an agent’s actions in production is a different job. The principle carries over: review works when reviewers know exactly what they are checking for.
ECO IA, the assistant Making Sense built inside Doppler’s marketing platform, runs the approval pattern in production. It reads live account data, diagnoses the account across seven dimensions, writes branded campaign drafts and assembles multi-email flows, and every output lands in the platform’s editor as an editable draft, so the user decides what goes out. It reached production in under three months, 95% of the users who engaged with it came back, and the engagement included a monitoring dashboard covering usage, cost and error classification. Doppler is not a fintech or healthcare case, and it shows a pattern that carries into regulated workflows: AI-generated actions prepared inside a live system, with the final decision left to the user.
Agentic AI in fintech: where autonomy creates value
AI agents are already workable in fintech operations, with administrative and document-heavy workflows as the practical starting point: document intake and classification, identity verification packets, reconciliation exceptions, servicing follow-ups that wait for someone to get to them. The payoff is capacity. More documents through the same team, less rework, and exceptions that get picked up instead of waiting. How much of that lands depends on the workflow and how much human review it still needs.
Credit decisioning is possible too, and it carries a heavier burden. Under Regulation B, creditors must give specific reasons for adverse actions, and those reasons have to relate to and accurately describe the factors actually considered. The obligation holds when automated models are involved. An agent that assembles the file and routes the case does less, and it still touches financial data, so the same controls apply. An agent whose reasoning cannot be traced back to nameable factors creates a notification problem the lender owns.
Auto Approve is useful as context. The constraint was a call center drowning in volume on peak days, with interactions left incomplete. The work Making Sense did there was the layer underneath: a secure data pipeline, predictive models and automated reporting across a lending operation. No agent executed anything. That layer is the precondition, and an agent reasoning over data the operation does not trust produces confident output nobody can act on.
Agentic AI in healthcare: protecting PHI while reducing administrative work
In healthcare, AI agents belong in administrative workflows first, where actions can be reviewed, constrained and reversed. That makes them a practical starting point for healthcare organizations. Eligibility checks, prior authorization packets, intake, records retrieval, coordination between clinic and family. Clinical applications require a different level of validation, oversight and regulatory assessment.
Prior authorization is the timely example. Under CMS-0057-F, impacted payers generally must answer urgent requests within 72 hours and standard requests within seven calendar days, and those operational requirements took effect in 2026. The related interoperability API requirements generally begin in January 2027. The rule covers specified payers and medical items and services, with exclusions that include drugs and QHP issuers on the federal exchanges.
The obligations sit with payers rather than providers. Providers still have a reason to prepare, because assembling complete requests and handling exceptions matters more as electronic exchange expands. The rule requires processes and interoperability, not agents.
The harder requirement comes before the agent. Where protected health information reaches a vendor acting as a business associate, an agreement has to cover it and the architecture has to keep everything else out of scope. An agreement alone does not make a system compliant; access controls, risk assessment and the applicable safeguards do.
Opya was not an agent project. Making Sense took an autism clinic running entirely offline to three connected HIPAA-compliant applications, one for internal messaging, one for the clinical team and one for parents. Decisions about sensitive data, access and architecture got made at the start of that project, and agentic work puts the same decisions in the same place.
What to look for in an agentic AI partner for regulated industries
- Evidence of production experience. Which AI systems are live, what they do, and how much autonomy each one holds. A conversational assistant that writes drafts and a system that executes transactions are different builds.
- Experience with regulated workflows. How they handled sensitive data access, security review and integration with systems that predate the project. Our piece on choosing an AI implementation partner goes deeper into this for healthcare.
- Control over agent behavior. How permissions get defined, how each agent is identified, how credentials expire or get revoked, who approves what, what the execution log captures, and what happens when the system fails.
- Ownership after deployment. Who watches error rates, model changes, operating cost and performance once the engagement is over.
- Discovery before architecture. Whether the partner starts by mapping the workflow, its volume and its exception rate, and can say which processes do not justify an agent at all.
Making Sense’s published work shows AI integrated into live product workflows, with human control over generated outputs and operational monitoring. Projects in fintech and healthcare cover a separate capability: designing software around sensitive data, security and industry-specific requirements. A regulated agentic deployment brings those disciplines together.
How to scope a first agent for a regulated workflow
- Pick a reviewable process with real volume, one that passed the autonomy question above, where an error can be caught and corrected the same day.
- Write the evidence specification before the build. Define what the agent records, who can inspect it, and how long the information has to be retained.
- Run it in shadow mode long enough to cover the cases that matter. A high-volume queue surfaces common errors quickly. Workflows with monthly cycles or rare exceptions need a longer window, or a deliberate replay of historical cases.
- Measure more than agreement. A system can match human operators 98% of the time and still fail badly in the remaining 2%. Track error severity, exception volume, how often a person intervened, and performance on the riskiest cases.
- Grant write permissions on one action, then widen.
Governance is part of this process from the start, and we laid out a working version in our guide to AI governance for mid-market and PE-backed companies.
From compliance requirements to operational value
The business case gets measured at the workflow level: time per completed case, exception rates, manual review hours, rework, and the cost of running and monitoring the agent itself. Faster execution counts only if the process stays accurate and the controls do not consume the value the automation creates.
The question worth putting to a regulated workflow is how much autonomy it can safely support, what evidence that autonomy has to produce, and whether the operational gain justifies the controls required to run it.
If you are scoping a first agent in a regulated operation, the agentic AI solutions team at Making Sense works through the data boundary, the oversight design and the first workflow before any build starts. Book a working session and bring the process you had in mind.
Frequently asked questions
Can AI agents operate in HIPAA-regulated healthcare environments?
Yes, when the implementation satisfies applicable HIPAA requirements: access controls, safeguards, risk assessment, business associate agreements where required, and oversight suited to the workflow. Administrative workflows are the common starting point.
Can AI agents make credit decisions?
Automated systems can support or make credit decisions. The lender remains responsible for applicable lending law, including Regulation B’s requirement to give specific reasons for adverse actions that accurately describe the factors considered, so the reasoning behind a decision has to be traceable.
What should a company ask an agentic AI partner to show before trusting them with a regulated workflow?
Ask for evidence of live AI deployments, documented experience with regulated data, and a clear explanation of how the partner handles permissions, human approvals, security testing and monitoring after launch. Each case study should make clear what the AI system actually does and which actions remain under human control. Making Sense answers that with Auto Approve in lending, HIPAA-compliant applications for Opya in healthcare, and production AI inside Doppler’s platform.
How should companies control an AI agent’s access to internal systems?
AI agents for business should each get their own identity, with permissions limited to the task. Use short-lived credentials where appropriate, and revoke access when the task or the authorization ends. Avoid shared credentials and unrestricted access to sensitive systems.
What has to be logged for an AI agent to pass an audit?
Tool calls and write actions in sequence, outputs, model and system version, and who approved or overrode each high-impact action. Retention should follow the organization’s policy and applicable regulation, without retaining unnecessary data.
Which decisions should AI agents not make autonomously in regulated industries?
AI agents should not execute high-impact actions without appropriate safeguards, make clinical decisions beyond their validated and authorized scope, or make credit decisions that cannot satisfy applicable explanation requirements.
Oct 20, 2026